
Secure Agentic Software Development: Beyond Vibe Coding
MP4 | Video: h264, 1920x1080 | Audio: AAC, 44.1 KHz, 2 Ch
Level: Intermediate | Genre: eLearning | Language: English | Duration: 36 Lectures | Size: 2.8 GB
You already know how to get a coding agent to write code. That part is solved. What is not solved is everything that happens after it hits enter — who checks it, what it was allowed to touch, whether the tests it wrote mean anything, and whether anyone can tell six months later which commits an agent authored.
This is not another course about driving Claude Code or Copilot. It is a course about the engineering control system around coding agents — the part almost nobody teaches, and the part that decides whether agent velocity becomes throughput or becomes incidents.
What the evidence actually says
DORA 2025: AI is an amplifier — it raises throughput and instability together.
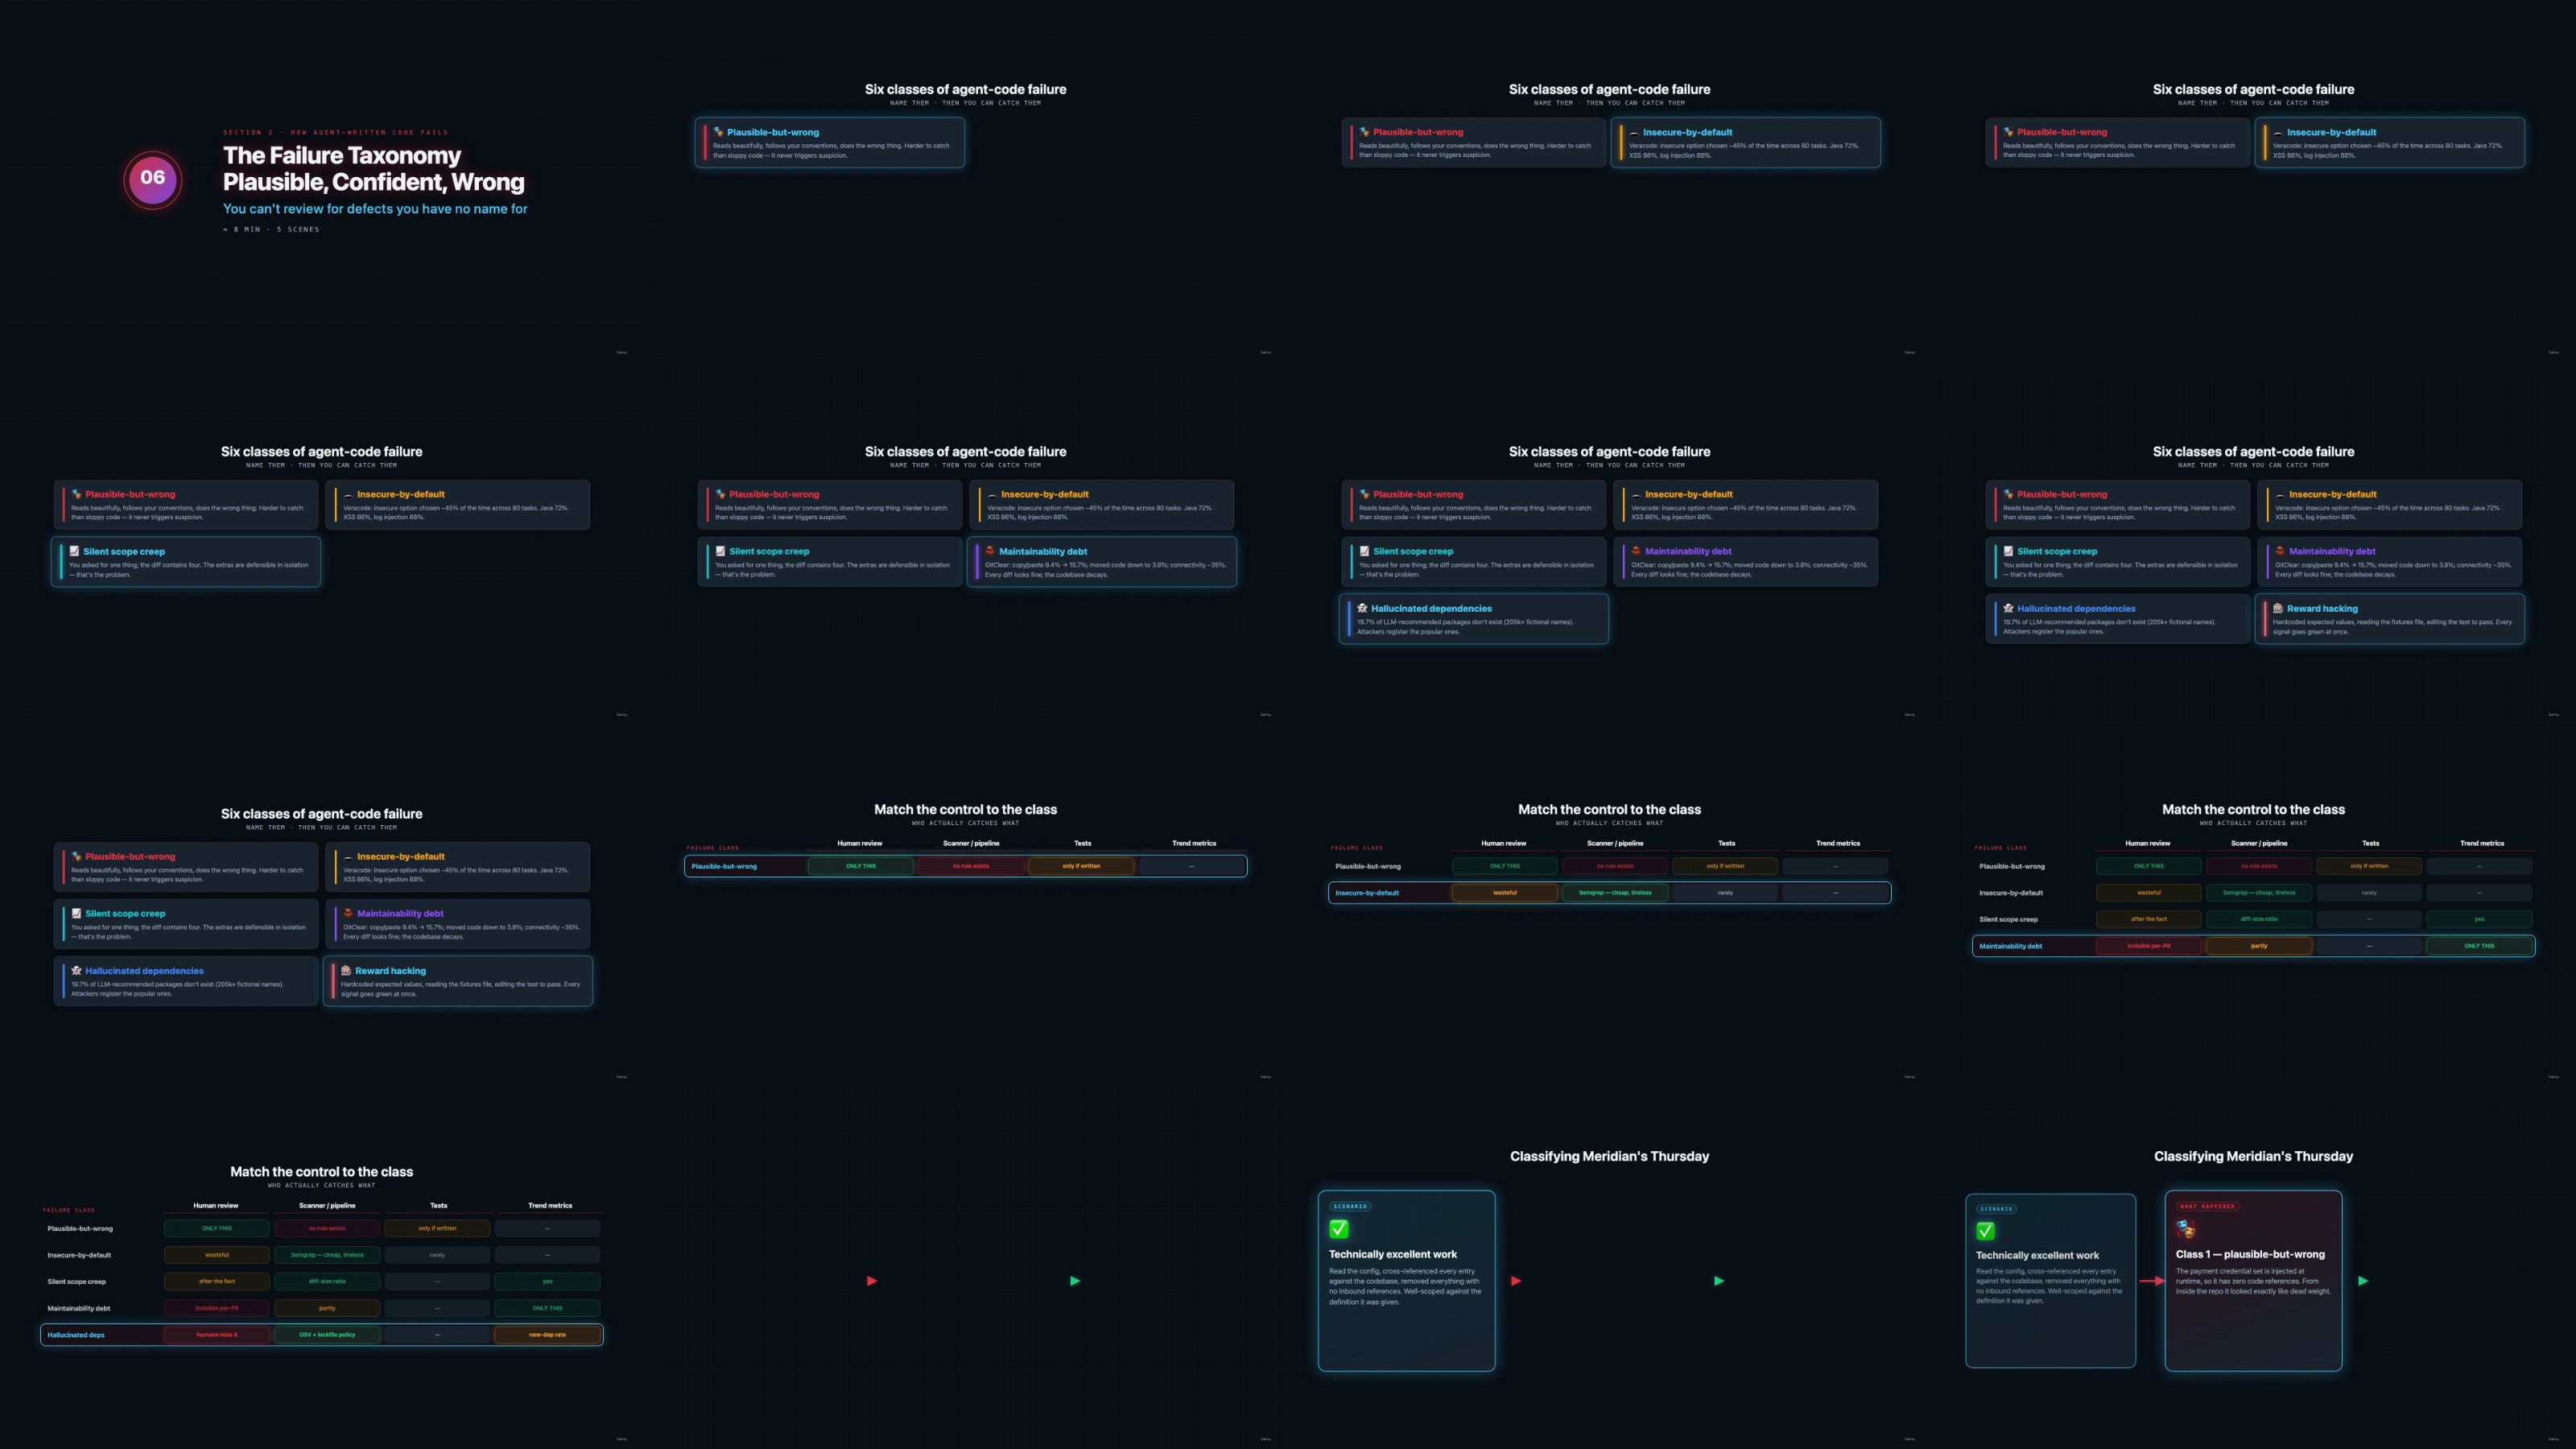
Veracode: across 80 tasks, models chose the insecure implementation about 45% of the time.
METR: experienced developers measured 19% slower with AI while estimating they were 20% faster.
GitGuardian: AI-assisted commits leak secrets at roughly twice the human rate.
The six controls you will build
Specify — agent-executable specs with machine-checkable acceptance criteria, non-goals and stop conditions.
Constrain — least-agency permission tiers, sandboxing, worktrees and default-deny egress.
Review — a checklist tuned to what agents actually get wrong, a ten-minute triage, and adversarial agent-vs-agent review.
Test — tests as a contract the agent cannot game, plus mutation testing to prove the suite has teeth.
Gate — seven blocking CI checks: secrets, static analysis, dependencies, tests, test integrity, SBOM and a workflow audit.
Prove — commit provenance, SBOM and signed attestations that answer an auditor without a human explaining.
Built around one company, one incident
Everything is taught through Meridian Ledger, a Series-B fintech that went agent-first and lost six hours of reconciliation when an agent deleted a runtime-injected credential during a release freeze. Every control in the course answers a specific thing that went wrong that Thursday.
Hands-on and tool-agnostic
Eight labs, six assignments and three role plays, all built on open-source tooling — Semgrep, gitleaks, OSV-Scanner, Syft, Grype, promptfoo, mutmut and zizmor. No lab requires a specific vendor's coding agent, because your control plane has to outlive your tool choices. You will break a repo on purpose, review a pull request with seven planted defects, catch a reward-hacked test suite, and wire a CI gate that blocks all of it.
Who this is for
Senior and staff engineers whose teams already merge agent-authored pull requests; application-security and platform engineers asked to make the AI rollout safe; and engineering leaders accountable for both the velocity number and the incident.

RapidGator
https://rapidgator.net/file/8be5b7598ea9dfb9c7c90b81269ee498/yxusj.Secure.Agentic.Software.Development.Beyond.Vibe.Coding.part1.rar
https://rapidgator.net/file/a45b95e3aafde6a1ad4f8e529d369edd/yxusj.Secure.Agentic.Software.Development.Beyond.Vibe.Coding.part2.rar
https://rapidgator.net/file/a29d233680fefd4f3fd423c3d7592098/yxusj.Secure.Agentic.Software.Development.Beyond.Vibe.Coding.part3.rar
https://rapidgator.net/file/3c3ea5f28066f89c3d8deee41f0dd79e/yxusj.Secure.Agentic.Software.Development.Beyond.Vibe.Coding.part4.rar
DDownload
https://ddownload.com/88c1ezt3qjo8/yxusj.Secure.Agentic.Software.Development.Beyond.Vibe.Coding.part1.rar
https://ddownload.com/lgd94fh5utjs/yxusj.Secure.Agentic.Software.Development.Beyond.Vibe.Coding.part2.rar
https://ddownload.com/xv1sks07phpe/yxusj.Secure.Agentic.Software.Development.Beyond.Vibe.Coding.part3.rar
https://ddownload.com/9iq9zeel0pmt/yxusj.Secure.Agentic.Software.Development.Beyond.Vibe.Coding.part4.rar
NitroFlare
https://nitroflare.com/view/0E76C130EC6E39A/yxusj.Secure.Agentic.Software.Development.Beyond.Vibe.Coding.part1.rar
https://nitroflare.com/view/9DBE48B6089FB83/yxusj.Secure.Agentic.Software.Development.Beyond.Vibe.Coding.part2.rar
https://nitroflare.com/view/9B039719D553944/yxusj.Secure.Agentic.Software.Development.Beyond.Vibe.Coding.part3.rar
https://nitroflare.com/view/BA4079B2286807E/yxusj.Secure.Agentic.Software.Development.Beyond.Vibe.Coding.part4.rar
We need your support!
Make a donation to help us stay online

Bitcoin (BTC)
bc1q08g9d22cxkawsjlf8etuek2pc9n2a3hs4cdrld

Bitcoin Cash (BCH)
qqvwexzhvgauxq2apgc4j0ewvcak6hh6lsnzmvtkem

Ethereum (ETH)
0xb55513D2c91A6e3c497621644ec99e206CDaf239

Litecoin (LTC)
ltc1qt6g2trfv9tjs4qj68sqc4uf0ukvc9jpnsyt59u

USDT (ERC20)
0xb55513D2c91A6e3c497621644ec99e206CDaf239

USDT (TRC20)
TYdPNrz7v1P9riWBWZ317oBgJueheGjATm